Penetration Testing Services in Illinois
Understand where security weaknesses exist across your Illinois environment before they can be exploited by attackers or identified during an audit. Every engagement is customized to your organization's technology estate and delivered with practical findings that help reduce risk across applications, networks, cloud environments, and business-critical systems.
A Generic Vulnerability Scan Won't Tell You What an Attacker Actually Sees
As organizations across Illinois continue adopting cloud platforms, third-party services, hybrid infrastructure, and remote access technologies, their attack surface becomes increasingly complex. Although automated vulnerability scans can identify known weaknesses, they cannot demonstrate how multiple vulnerabilities could be combined to compromise business systems, applications, or sensitive information.
Completing a penetration test solely to satisfy compliance requirements does not reveal how an attacker could move through your environment, target business-critical assets, or gain access to sensitive customer data. Manual penetration testing provides the attacker's perspective needed to validate real-world risk before it results in a security incident.
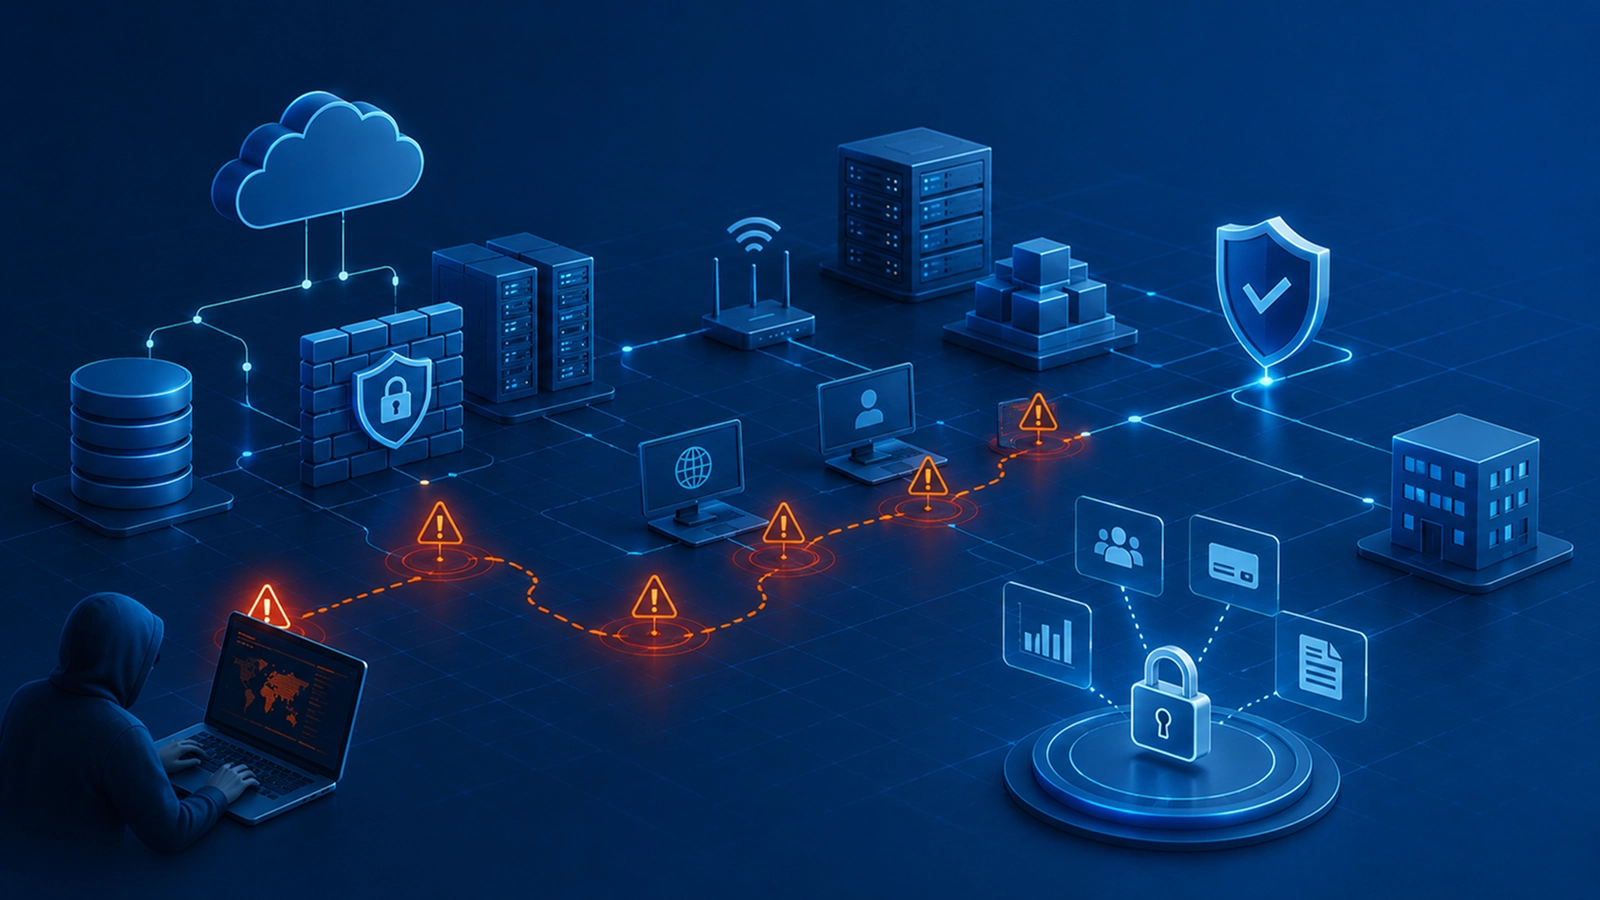
Evaluate the Systems That Matter Most to Your Business

Gain Visibility Across Your Attack Surface
Understand how an attacker could move across your internal network, cloud infrastructure, remote access points, and connected environments before they become opportunities for compromise.

Secure Critical Business Applications
Your customer-facing portals, internal applications, and APIs are assessed to identify vulnerabilities that could expose sensitive data, disrupt operations, or impact business continuity.

Assess Cloud Security Configurations
Identify cloud misconfigurations, excessive permissions, and exposed services that attackers could use to access workloads, data, or connected business systems.

Improve Compliance Readiness
Receive findings mapped to recognized security and compliance frameworks, helping your team prioritize remediation and prepare for regulatory, customer, or third-party security assessments.
Choose the Right Penetration Testing Partner
Three Things You Get on Every Engagement

Every assessment is led by senior penetration testers with hands-on experience across modern enterprise environments. The result is practical, validated findings based on real attack techniques, not automated scan results.

Your final report combines executive-level risk summaries with technical remediation guidance, making it easier for leadership to understand business impact while giving technical teams the detail needed to fix vulnerabilities efficiently.

Security doesn't end with the report. Once remediation is complete, we perform a retest of Critical and High findings at no additional cost to confirm vulnerabilities have been successfully addressed, giving your team confidence before closing the engagement.
Security Improvements Start With Actionable Results
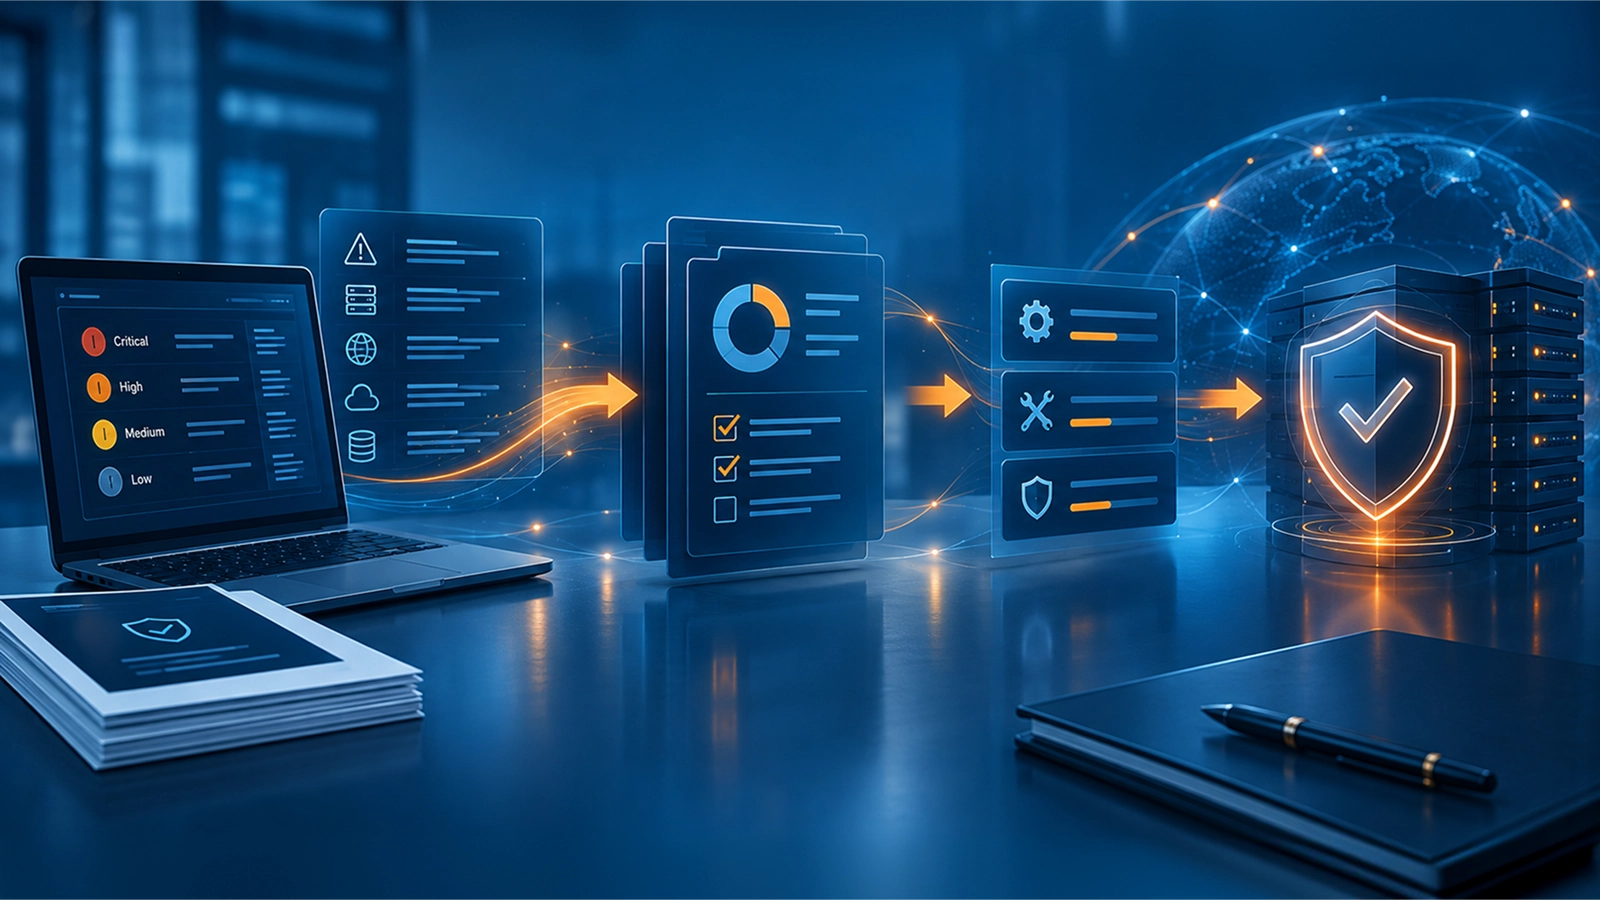
A penetration test delivers value only when findings lead to meaningful improvements. Every engagement is designed to help your team understand which vulnerabilities present the greatest business risk, why they matter, and how they should be prioritized for remediation, without overwhelming you with unnecessary technical noise.
A practical, risk-based approach helps your team focus resources where they matter most. Our findings are translated into clear, actionable recommendations your security and IT teams can use to drive remediation. We help you understand not just what is vulnerable, but how an issue could impact your business and what to address first. The result is a clearer path from penetration testing findings to measurable security improvements.
Common Questions Asked By Illinois Buyers
How often should my organization perform a penetration test?
Most organizations should perform a penetration test at least annually and after significant infrastructure changes, application releases, cloud migrations, or major network modifications. Regular assessments also help maintain compliance and identify new security risks as your environment evolves.
What is included in a penetration testing engagement?
A typical engagement includes reconnaissance, vulnerability validation, manual exploitation, risk analysis, detailed reporting, and remediation recommendations. Depending on your requirements, testing can cover networks, web applications, mobile applications, cloud environments, APIs, wireless infrastructure, and internal systems.
How is a penetration test different from a vulnerability scan?
A vulnerability scan automatically identifies known weaknesses, while a penetration test validates exploitability through manual testing. This provides a more accurate understanding of business risk by identifying attack paths, chained vulnerabilities, and security gaps that automated tools may miss.
Will penetration testing disrupt our business operations?
Penetration testing is planned around operational risk, with agreed rules of engagement, defined testing boundaries, and clear stop points. Our team works closely with stakeholders to minimize disruption while still validating meaningful security risks. Where sensitive or operational environments are involved, testing can use read-only checks and additional safeguards. No test should touch a live control system without written approval and the appropriate technical stakeholders involved.
Can penetration testing help with compliance requirements?
Yes. Penetration testing can support regulatory, contractual, and security assessment requirements by identifying vulnerabilities and providing documented findings for remediation. For PCI DSS, Requirement 11.4 calls for internal and external penetration testing at least every 12 months and after significant changes to the cardholder data environment, with retesting after remediation. Our penetration testing methodology follows recognized approaches including NIST SP 800-115 and PTES.
How long does a penetration testing engagement typically take?
The duration depends on the size and complexity of your environment. Most engagements are completed within two to four weeks, including planning, testing, reporting, and a final walkthrough of findings.
What will our final penetration testing report include?
Your engagement documentation includes three key deliverables: a Risk Impact Brief for leadership, a Technical Pentest Report for the security team, and an Attestation Letter for the auditor. Together, these documents provide business context, technical findings, supporting evidence, risk details, remediation guidance, and formal documentation needed to understand and act on the results.
What Illinois-specific security requirements should organizations consider when planning a penetration test?
Illinois organizations may need to consider requirements related to reasonable data security, vendor relationships, and protection of sensitive information. The Illinois Personal Information Protection Act (PIPA) establishes requirements around reasonable security measures and contracts with vendors handling personal information, while the Biometric Information Privacy Act (BIPA) includes a standard of care for biometric information. A penetration test can help organizations identify security weaknesses relevant to these obligations, although testing alone does not establish compliance.