Cloud Penetration Testing Methodology
Cloud environments can change faster than security teams can review them. Our cloud penetration testing methodology examines Amazon Web Services (AWS), Microsoft Azure, and Google Cloud environments, assessing how identities, permissions, configurations, exposed services, workloads, and connected resources interact to create opportunities for compromise. We go beyond checking individual weaknesses to determine how those weaknesses could be combined to reach sensitive resources, escalate access, or move deeper into your cloud environment.
One Cloud Misconfiguration Can Open a Path to Everything Behind It
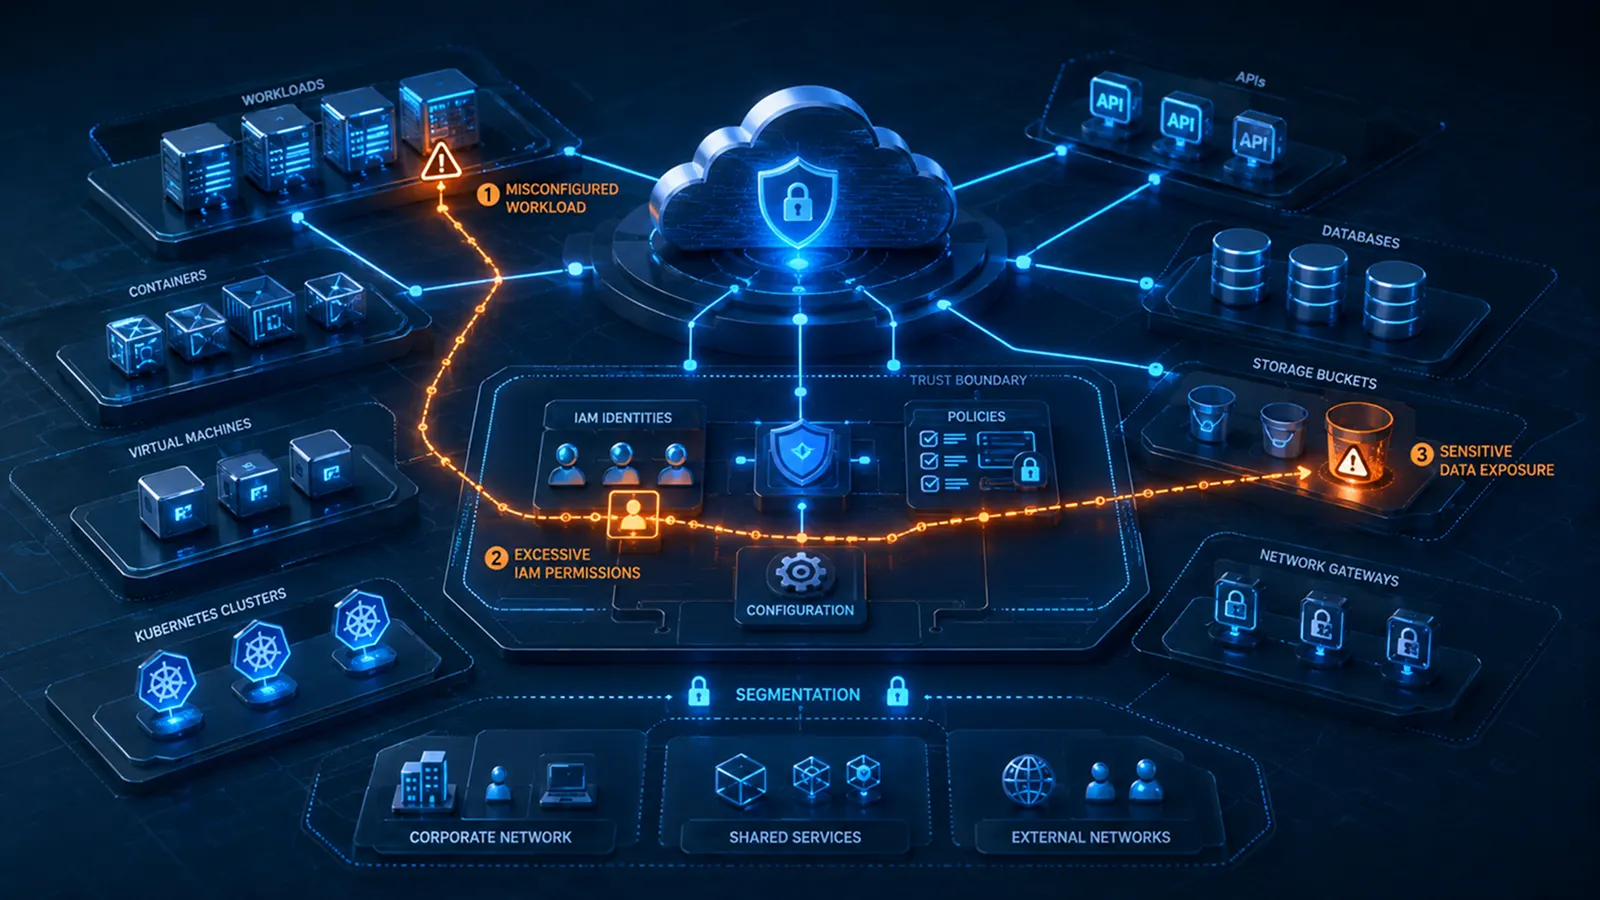
Cloud security issues rarely exist in isolation. An exposed workload reaches a storage bucket. It inherits rights it should not have. Those rights open a path to sensitive data. That is not three separate findings. It is one attack path.
Instead of treating each weakness as a separate finding, we trace how an attacker could chain them together and determine what that path could actually expose. Our methodology draws on established penetration testing practices, including PTES and NIST SP 800-115, while incorporating cloud-specific security considerations across identities, permissions, configurations, workloads, and connected services.
Test the Cloud Controls That Keep Your Environment Connected and Protected

Challenge Identity and Privilege Boundaries
Assess IAM roles, service accounts, federation, privilege inheritance, and permission paths to determine whether an account or workload can obtain access beyond what it should.

Expose Misconfigured Cloud Services
Examine publicly accessible resources, security groups, storage permissions, exposed management interfaces, and configuration weaknesses that could create unintended entry points into your cloud environment.

Protect Cloud Data and Workloads
Test whether sensitive data, databases, object storage, virtual machines, and other cloud workloads can be reached or manipulated through compromised credentials, excessive permissions, or exposed services.

Trace Paths Across Connected Cloud Resources
Evaluate how identities, applications, APIs, workloads, containers, and cloud services interact to find escalation paths that could allow an attacker to move from an initial foothold toward higher-value resources.
Find Out Where Your Cloud Security Posture Stands
Know Where Your Cloud Environment Creates Exposure

Map how users, roles, service accounts, and permissions interact across your cloud environment to identify access relationships that could create unnecessary exposure.

Identify security-relevant weaknesses across cloud services, storage, networking, workloads, and exposed interfaces that could increase your attack surface.

Evaluate how cloud resources connect with applications, APIs, identities, data stores, and other environments so security teams can understand where one weakness could affect a wider part of the environment.
Know What Needs Attention Before Cloud Risk Becomes Business Risk
Your cloud environment can contain thousands of resources, permissions, workloads, and connections. A penetration test gives your team a clearer picture of which security weaknesses can be exploited, and which ones deserve attention first.
You'll leave the engagement with evidence-backed findings, a clearer understanding of their potential impact, and practical direction for what should happen next. That means your security team can focus its time on the exposures that matter instead of trying to interpret a long list of cloud configuration issues.
Common Questions About Cloud Penetration Testing
Do we need permission from our cloud provider before penetration testing?
In most cases, prior approval is not required when testing cloud resources that your organization owns, and that are covered by the provider's permitted testing policies. AWS, Microsoft Azure, and Google Cloud each publish rules governing security testing of customer-owned environments. Testing must remain within your authorized resources and must not target the cloud provider's infrastructure or another customer's environment. Certain disruptive testing techniques may require additional approval or coordination with the provider.
How long does a cloud penetration testing engagement take?
Most engagements take two to four weeks, depending on the size and complexity of the environment, testing scope, and number of cloud services involved. The timeline is established during scoping, so your team knows what to expect before testing begins.
Will cloud penetration testing disrupt our operations?
Testing is planned around your operational requirements and agreed rules of engagement. The objective is to identify meaningful security weaknesses while keeping the assessment controlled and minimizing unnecessary disruption.
What cloud environments can you test?
The scope can be tailored to the cloud platforms, services, workloads, and supporting infrastructure your organization uses. Testing can focus on a single environment or span connected cloud resources when the broader architecture needs to be evaluated.
How do you determine what should be included in the test?
Scope is determined based on your cloud architecture, business-critical assets, exposure, testing objectives, and the risks your team wants to validate. This ensures the engagement focuses on testing effort where it can provide the greatest value.
Can cloud penetration testing support compliance requirements?
Yes. A cloud penetration test can provide security evidence and findings that support compliance and risk-management initiatives such as PCI DSS, HIPAA, SOC 2, and ISO 27001. The specific requirements supported depend on your organization's regulatory obligations, cloud environment, and agreed assessment scope.
What happens if you find a critical vulnerability during testing?
Critical findings are communicated according to the agreed engagement process rather than waiting until the final report. This allows your team to understand and respond to significant risks while the assessment is still underway.
What will we receive at the end of the engagement?
You'll receive detailed engagement deliverables covering validated findings, their potential impact, supporting evidence, risk prioritization, and remediation guidance. One retest is included at no additional cost for Critical and High findings after remediation. The results are presented so both technical and business stakeholders can understand what was found and what requires attention.
Can you test cloud environments that connect with our internal systems?
Yes. Where those connections are included in scope, testing can consider how cloud resources interact with internal infrastructure, applications, identities, and other connected systems. This helps provide a more complete view of risks created across the environment.
When should we perform a cloud penetration test?
Organizations should perform cloud penetration testing at least once a year and after significant changes such as major cloud migrations, architectural changes, new externally accessible services, or the movement of important workloads into the cloud. Testing should also be considered whenever significant changes could introduce new attack paths or security risks.
How is cloud penetration testing different from a cloud security assessment?
A cloud security assessment generally evaluates security controls, configurations, and posture against defined requirements. Penetration testing goes further by attempting to validate whether identified weaknesses can actually be exploited and what an attacker could potentially achieve.