AI-Powered Penetration Testing Methodology
Combine AI-assisted analysis with expert-led penetration testing to identify attack paths, prioritize security risks, and accelerate the assessment process. Our methodology uses AI to analyze complex security data while penetration testers validate findings and apply real-world security expertise, giving your team broader coverage and practical insights you can act on.
AI Handles the Scale. Experts Handle the Decisions.
Modern environments generate more security data than manual analysis alone can efficiently process. AI-assisted penetration testing accelerates the identification of attack paths, correlates related vulnerabilities, and helps prioritize the risks most likely to impact your business before valuable testing time is lost.
Security specialists review AI-generated results to confirm accuracy, investigate potential attack scenarios, rule out false positives, and based on how your environment operates. The result is broader coverage, faster insights, and a report your team can confidently use to strengthen its security posture.
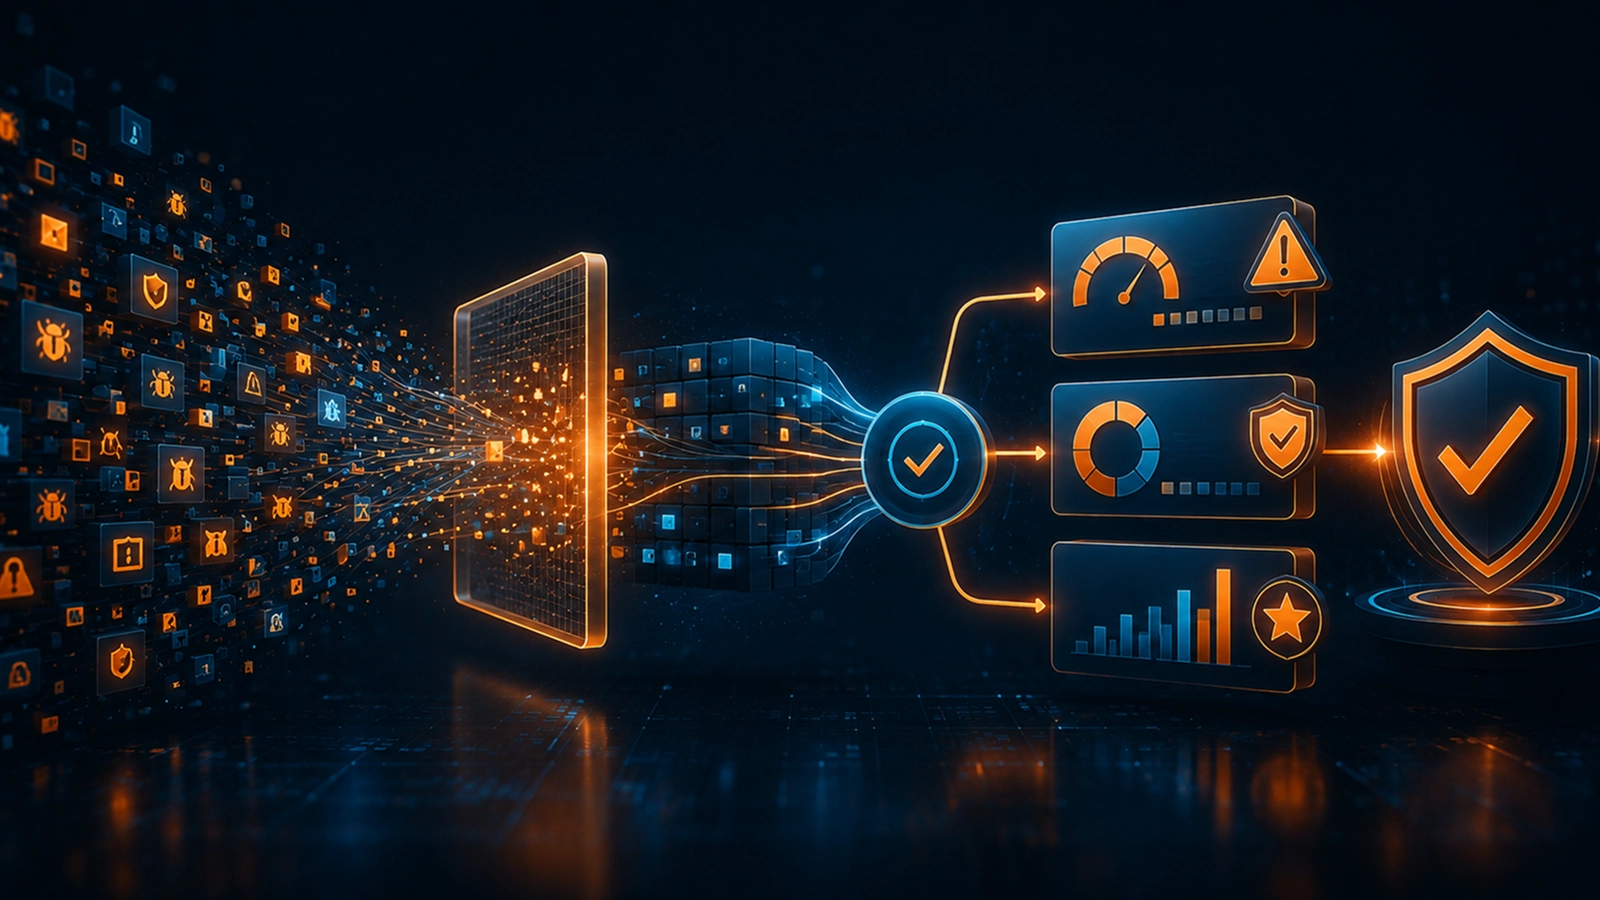
How AI Strengthens the Testing Process

See More Than Traditional Testing Alone
AI-assisted analysis helps identify exposed assets, interconnected systems, and potential attack paths across your environment, giving your penetration test broader visibility from the very beginning.

Focus on the Vulnerabilities That Matter Most
Rather than overwhelming your team with hundreds of findings, AI helps prioritize vulnerabilities based on exploitability and business impact, so remediation efforts begin where they'll have the greatest effect.

Validate the Findings That Matter Most
AI accelerates analysis by identifying patterns, correlations, and potential attack paths. Findings are reviewed against the engagement scope and testing evidence before they are prioritized in the final report.

Understand What to Fix First
The assessment delivers a Risk Impact Brief for leadership, a Technical Pentest Report for security teams, and an Attestation Letter for audit and compliance needs. Each connects findings to business impact.
Understand What Your Penetration Testing Report Is Really Telling You
Turn Testing Results into Security Priorities

Your report highlights the vulnerabilities that present the greatest business risk, helping your team focus on remediation efforts where they'll have the most impact instead of working through an unprioritized list of findings.

Your report connects security findings with supporting evidence, business impact, and remediation priorities, making it easier for your team to understand which issues require attention first.

Receive clear remediation recommendations, business context, and prioritized next steps that help your security, IT, and leadership teams make faster, more informed decisions.
Turn Security Findings into Better Decisions
A penetration testing report should do more than document vulnerabilities; it should help your team understand what poses the greatest risk to your business. Our AI-assisted methodology organizes findings by exploitability, business impact, and remediation priority, making it easier to focus on what matters most.
AI helps organize and accelerate the assessment, while experienced testers review every significant result before it reaches your report. Each recommendation is presented with the technical context and business relevance needed to help teams make informed remediation decisions.
Common Questions About AI-Assisted Penetration Testing
What is AI-assisted penetration testing?
AI-assisted penetration testing uses artificial intelligence to analyze security data, identify potential attack paths, correlate vulnerabilities, and prioritize higher-risk findings during an assessment. This helps testing teams process complex environments more efficiently and focus assessment effort on the areas most relevant to business risk.
Which parts of penetration testing benefit most from AI?
AI accelerates tasks such as attack surface analysis, vulnerability correlation, and risk prioritization, allowing penetration testers to focus on validating real-world exploitability rather than reviewing repetitive data. This results in broader security coverage, faster insights, and reports that prioritize the vulnerabilities most relevant to your organization.
Can AI replace traditional penetration testing?
No. AI enhances penetration testing but does not replace the broader testing methodology. AI can accelerate analysis, correlation, and prioritization, but penetration testing still requires controlled testing, exploit validation, business-context analysis, and actionable remediation recommendations.
Does AI-assisted penetration testing reduce false positives?
Yes. AI helps prioritize potential security issues and identify patterns across large volumes of security data. Findings are then reviewed against testing evidence before reporting, which helps reduce false positives so reported findings more accurately reflect the security risks identified during the assessment.
Can AI-assisted penetration testing support compliance requirements?
Yes. AI supports the assessment process by improving analysis and prioritization, while the engagement follows established penetration testing methodologies aligned with applicable compliance requirements. Depending on your scope, the final report can support frameworks and standards such as PCI DSS, HIPAA, SOC 2, ISO 27001, and the NIST Cybersecurity Framework.
Can AI-assisted penetration testing evaluate Large Language Models (LLMs) and AI integrations?
Yes. AI-focused penetration testing can assess LLM applications and connected AI systems for risks such as prompt injection, sensitive information disclosure through model responses, insecure AI integrations, and excessive access by AI agents or connected tools. Testing can also evaluate how AI systems interact with APIs, data sources, applications, and other connected services to identify attack paths that could create security or business risk.